
· Michal Pietrus
Available in: EN
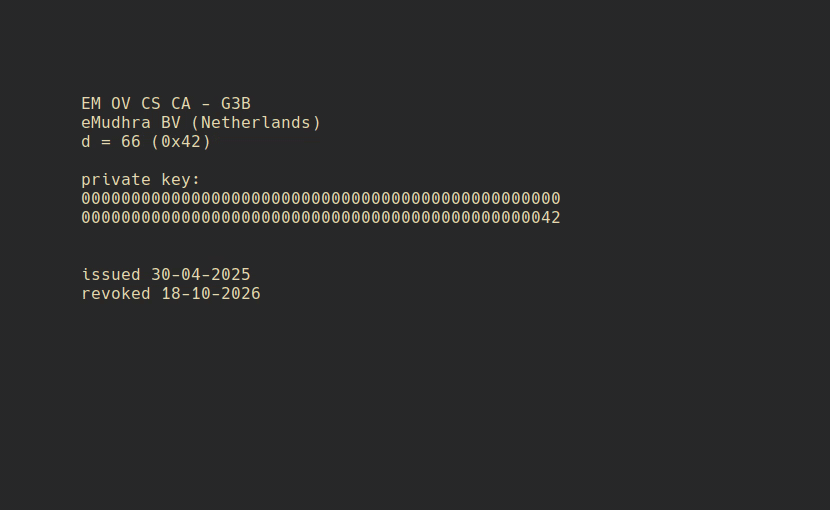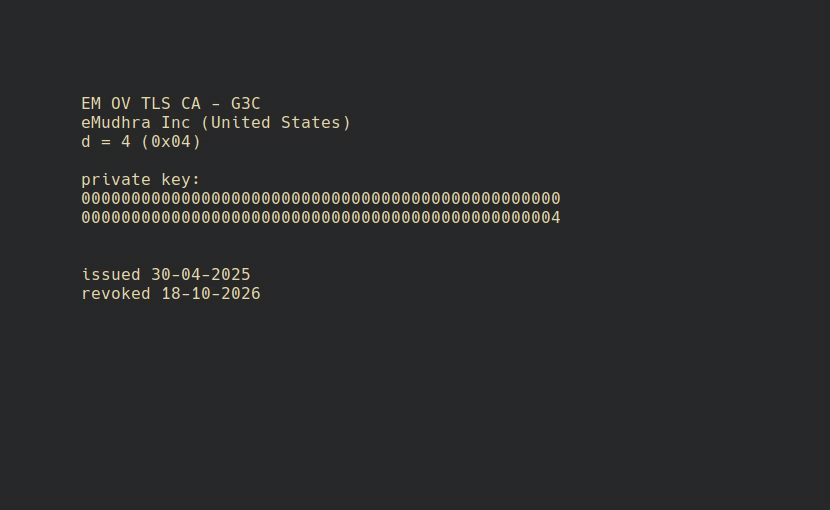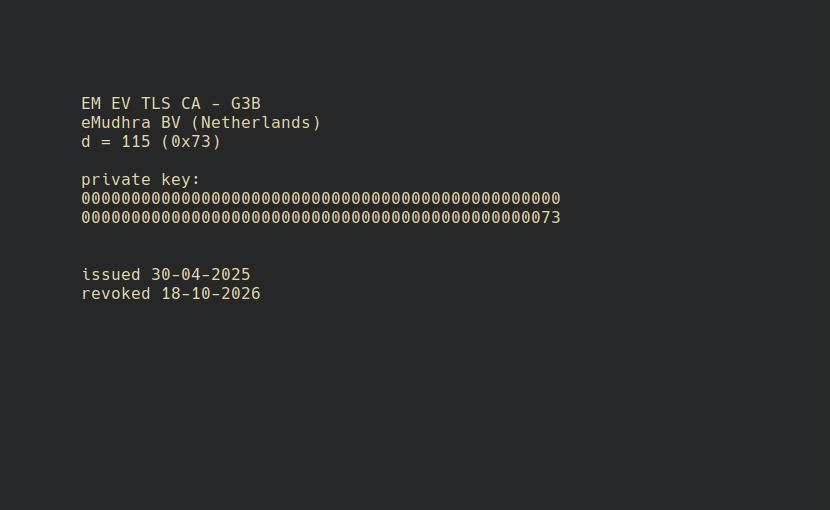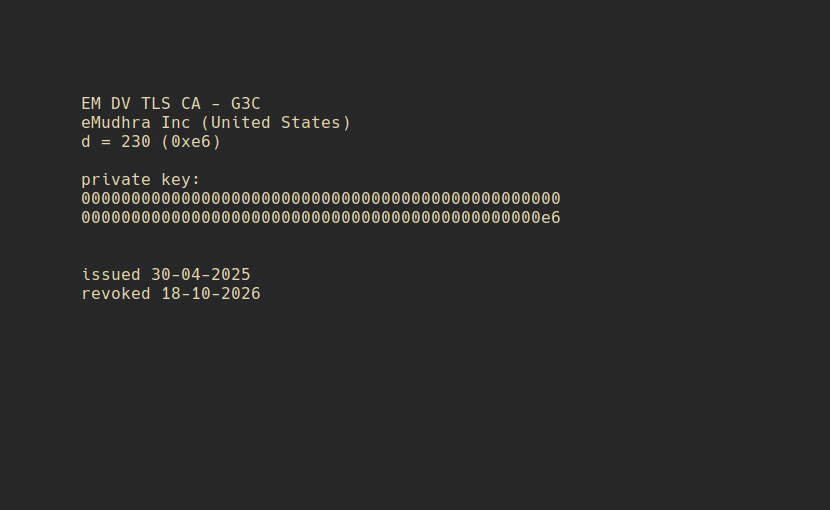
Eight weak private keys. One global trust problem.
Eight compromised CA keys, an entire root removed from browser trust stores, and 30000+ certificate issuances affected. The eMudhra incident raises a bigger question: why should compromising one signing key undermine an entire chain of trust? Is there any other option?